
Shadow AI and How Unapproved Tools Can Expose Business Data
An employee asks a public AI assistant to summarize a customer contract. A manager uploads a spreadsheet to build a forecast. A developer connects a coding assistant to a repository. Each action may save time, but it can also move sensitive business data into a service the company has never reviewed, configured, or approved.
That is the central shadow AI security problem. Shadow AI is the use of artificial intelligence tools, accounts, browser extensions, application features, or automated agents outside an organization’s approved technology and governance process. The employee may have a legitimate business goal. The risk comes from the missing review: security and privacy teams may not know what data entered the tool, how long the provider retains it, whether it can be used to improve a model, where it is processed, who can access it, or which other systems the tool can reach.
A blanket ban rarely solves the problem. People adopt AI because it removes real friction from research, writing, analysis, customer service, software development, and routine administration. If the approved path is unclear or slow, use often continues through personal accounts and free tools. A stronger response gives employees a safe way to use AI while the business controls data, access, vendors, and accountability.
What Shadow AI Includes
Shadow AI is broader than a public chatbot. It includes any unapproved or unmanaged AI capability used for company work. Some products are obvious, such as a standalone writing assistant. Others arrive quietly as an AI feature inside software the business already licenses.
- Public generative AI tools accessed through personal or free accounts
- AI meeting assistants that record, transcribe, or summarize calls
- Browser extensions that can read web pages, email, or form content
- Coding assistants connected to source code, tickets, logs, or developer tools
- AI features enabled inside customer relationship, productivity, design, finance, or human resources platforms
- Custom bots and agents that connect to cloud storage, email, calendars, databases, or collaboration platforms
- AI tools bought directly by a department with a credit card and no security review
The distinction that matters is governance, not the tool’s brand. A widely used service can still create risk when employees use the wrong account type, enable an unreviewed connector, or enter information that the approved use case does not permit. Conversely, a properly reviewed tool may be suitable for some tasks and data classes but prohibited for others.
How AI Data Leakage Happens
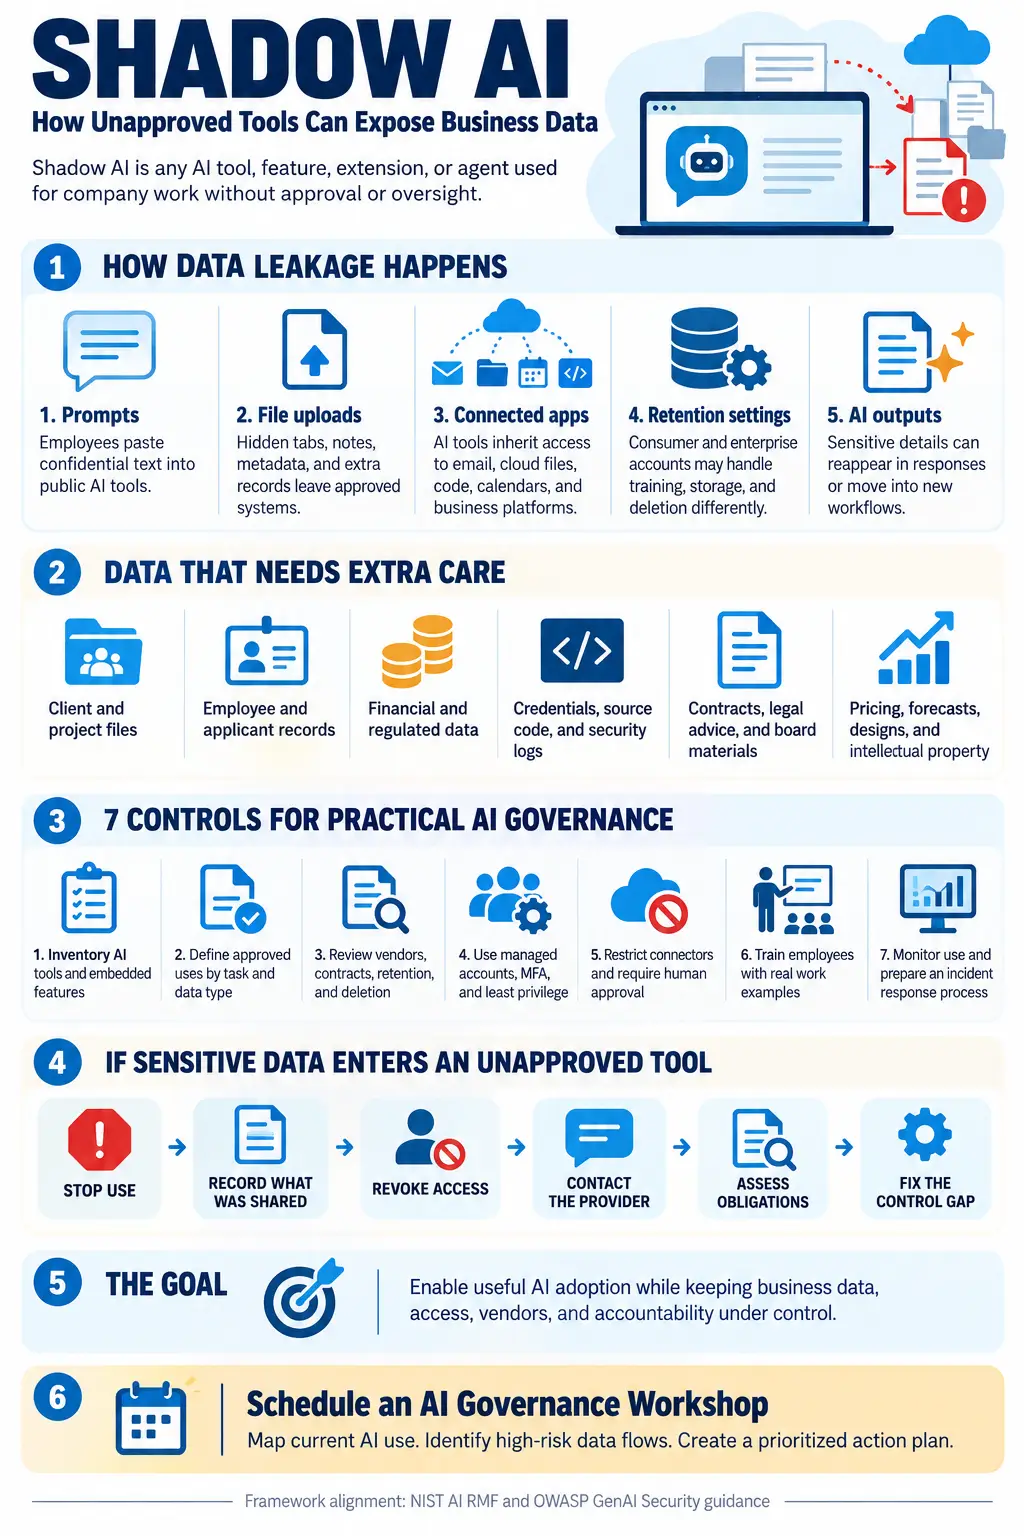
AI data leakage occurs when information moves outside its intended boundary or becomes accessible, reusable, or discoverable in a way the organization did not authorize. The leak does not have to appear in a public search result to matter. Loss of control over confidential data, weak access restrictions, or an inability to meet a deletion request can create operational, contractual, privacy, and regulatory exposure.
Employees paste confidential information into prompts
The simplest path is direct input. A user pastes an email thread, contract clause, customer complaint, incident log, patient note, employee record, or financial result into an AI assistant. The prompt may contain names, account numbers, pricing, credentials, protected health information, personally identifiable information, or trade secrets. Even when the requested output is harmless, the input can violate internal handling rules or commitments made to customers and partners.
File uploads reveal more than the user intended
Documents and spreadsheets often contain hidden or overlooked data. A workbook may include formulas, comments, hidden tabs, customer identifiers, or historical records. A presentation may contain speaker notes. A document can carry revision history or embedded metadata. Uploading the whole file to answer one question expands the exposure beyond the information the employee meant to share.
Connected tools inherit broad access
Modern AI assistants can connect to mailboxes, shared drives, source-code repositories, customer platforms, calendars, and internal knowledge bases. If a connector receives broader permissions than the task requires, the AI system can retrieve or act on data across a much larger area. OWASP describes excessive agency as a combination of excessive functionality, permissions, or autonomy. Its guidance recommends limiting extensions and permissions, enforcing authorization in downstream systems, requiring human approval for high-impact actions, and monitoring activity.
Retention and training settings are misunderstood
Consumer, team, and enterprise versions of the same product may have different terms, controls, retention periods, training defaults, administrative visibility, and deletion options. These details also change. Employees should not assume that a paid subscription automatically provides the organization’s required protections. The business must review the current contract, privacy terms, security documentation, configuration, and data flows for the exact service and account type it plans to use.
Outputs can disclose or reproduce sensitive material
An AI application can expose sensitive information through its response if the underlying system, retrieval process, or access controls are poorly designed. The OWASP GenAI Security Project identifies personally identifiable information, financial details, health records, confidential business data, credentials, and legal documents as examples of sensitive information at risk. It recommends controls such as data sanitization, input validation, least privilege, restricted data sources, clear retention practices, user education, and tokenization or redaction where appropriate.
Prompts and outputs enter new workflows
A response may be copied into a customer email, policy, proposal, ticket, software release, or executive report. If the content contains confidential information, insecure code, unsupported claims, or material derived from a third party, the risk travels with it. Shadow AI therefore affects confidentiality, integrity, intellectual property, recordkeeping, and decision quality. Data loss prevention alone cannot address every part of the problem.
A Common Shadow AI Scenario
Consider a project manager preparing a bid or project handoff. The manager uploads subcontractor proposals, client requirements, and excerpts from project plans to an unapproved AI tool and asks it to identify scope gaps. The files include pricing, contact details, contract terms, project locations, and technical notes. The manager receives a useful comparison in minutes.
From the user’s perspective, the task is complete. From the company’s perspective, several questions remain unanswered. Were the client and subcontractor materials allowed to leave the approved systems? Did the provider retain the files or prompts? Could an administrator retrieve or delete them? Was the data processed in an acceptable location? Did a connector receive continuing access? Do the contracts restrict use by subprocessors? Can the company reconstruct what happened if a client asks?
The important lesson is that good intent does not replace control. The employee did not need to be careless or malicious. A normal productivity shortcut created risk because the organization had not defined an approved method for that use case.
Business Data That Should Trigger Extra Care
Each organization needs a data classification standard, but several categories should receive close scrutiny before they enter any AI system:
- Client, subcontractor, and project data, including communications, bids, contracts, plans, credentials, configurations, and support records
- Employee, applicant, payroll, benefits, disciplinary, and performance information
- Health, financial, payment, government identifier, and other regulated personal information
- Source code, architecture diagrams, vulnerabilities, logs, incident details, keys, tokens, and passwords
- Unreleased financial results, forecasts, pricing, strategy, merger activity, and board materials
- Legal advice, privileged communications, litigation material, and confidential agreements
- Research, product plans, formulas, methods, designs, and other intellectual property
The safest default is data minimization. Give an AI tool only the information required for an approved task. Replace real names and identifiers with synthetic or masked values when the task permits. Never treat a prompt as a private workspace unless the organization has verified the service, account, configuration, contract, and intended data use.
Signs That Shadow AI Is Already Present
Most organizations should assume that some unapproved AI use already exists. Useful indicators include new browser extensions, sign-ins to consumer AI domains, expense claims for small software subscriptions, unfamiliar OAuth grants, meeting bots joining calls, employees discussing AI-generated work, and departments building automations without IT involvement. A sudden policy announcement may drive this activity further out of sight if employees do not have an approved alternative.
Discovery should combine technical visibility with direct conversation. Review identity and access logs, cloud application discovery, endpoint and browser inventories, DNS or secure web gateway data, software expenses, OAuth grants, and vendor lists where lawful and appropriate. At the same time, ask teams which tasks they are trying to improve, which tools they use, what information they enter, and what prevents them from using an approved option. The goal is to understand business demand and risk, not to punish employees for revealing it.
Seven Controls for Practical AI Governance
NIST’s AI Risk Management Framework organizes AI risk work around four functions: Govern, Map, Measure, and Manage. The framework calls for mechanisms to inventory AI systems, clear roles, policies for third-party AI and data, documented human oversight, ongoing monitoring, and risk treatment based on impact and likelihood. A small or midsize business can translate those outcomes into the following control program.
Create an AI inventory
Record the AI tools and AI-enabled features the organization uses or is evaluating. For each entry, document the owner, users, business purpose, account type, vendor, data categories, integrations, permissions, decision impact, contract status, retention settings, and approval state. Include AI features embedded in existing software because they may introduce new data flows even when the underlying product is already approved.
Define acceptable use by data and task
A useful policy tells employees what they can do, what data they can use, which tools are approved, and when a review is required. Avoid vague instructions such as “do not enter sensitive data” unless the policy defines sensitive data with examples. Address meeting transcription, source code, customer content, personal information, legal material, automated decisions, external publication, and connections to company systems. Give employees a named contact and a quick path for proposing a new use case.
Review vendors and configurations
Evaluate the exact service tier and planned configuration. Review data use, training, retention, deletion, encryption, access controls, authentication, logging, incident notification, subprocessors, data location, intellectual property terms, and exit options. Confirm whether administrators can manage accounts and integrations. Revisit the review when a provider changes terms, adds an AI feature, or expands a connector’s capabilities.
Limit access and integrations
Use company-managed accounts, single sign-on, multifactor authentication, role-based access, and least privilege where supported. Restrict OAuth scopes and connectors to the minimum data and actions required. Separate experimental environments from production data. Require an independent approval step before an agent sends messages, changes records, publishes content, transfers money, modifies code, or performs another high-impact action.
Add data safeguards
Apply data classification and handling rules to AI workflows. Depending on the environment, safeguards may include blocking unsanctioned services, warning users before sensitive uploads, masking identifiers, scanning prompts and files, controlling copy and paste, encrypting approved data stores, and setting retention limits. Technical controls should support the policy, but they need testing because AI traffic, browser sessions, images, archives, and integrations can create visibility gaps.
Train employees with real examples
Training should show how ordinary work can expose data. Demonstrate why pasting a customer email, uploading a full spreadsheet, sharing a meeting transcript, or installing an AI extension may create risk. Teach employees to verify outputs before use and to report accidental disclosure quickly. Make the approved tools and request process easy to find. Short role-specific sessions for sales, finance, human resources, developers, and executives are usually more useful than one generic presentation.
Monitor and respond
Track approved AI use, new applications, unusual data transfers, connector permissions, policy exceptions, and reported incidents. Define what happens when someone enters sensitive information into an unapproved tool. The response may require preserving evidence, identifying the data and affected records, revoking tokens, contacting the provider, requesting deletion, reviewing contractual or legal obligations, notifying internal leaders, and closing the control gap. Test the process before a real event.
What to Do After a Suspected AI Data Leak
Act quickly, but do not erase the evidence needed to understand the event. Ask the employee to stop using the tool and record the service, account, date, prompts, files, output, integrations, and actions taken. Security should determine which information was exposed, whether the tool retained or shared it, and whether any credentials or tokens require rotation. The organization should review vendor deletion options and contact channels rather than assuming that deleting a chat from the user interface removes every copy.
Bring in the appropriate privacy, legal, compliance, human resources, customer, insurance, and leadership contacts based on the data and circumstances. Notification duties depend on the information, contracts, locations, industry, and applicable law, so the company should seek qualified legal advice rather than rely on a generic AI policy. After containment, update the tool inventory, use-case decision, training, and technical controls so the same path is less likely to recur.
Why a Ban Is Not an AI Governance Program
Blocking every AI domain may reduce some casual use, but it does not cover embedded features, mobile devices, personal accounts, browser extensions, or approved platforms that add new AI capabilities. It can also prevent the organization from learning which use cases employees value. A policy that only says no gives people no safe route to complete legitimate work.
Practical governance sets boundaries and makes approved use easier. It pairs a short list of sanctioned tools with data rules, vendor review, access controls, human oversight, monitoring, and an exception process. Leaders can then compare productivity benefits with confidentiality, privacy, security, intellectual property, and decision risks. Some uses will be approved, some will need safeguards, and others should remain prohibited.
Start With an AI Governance Workshop
Shadow AI security becomes manageable when leadership, IT, security, privacy, legal, and business teams agree on the first decisions. An AI governance workshop can identify current tools and use cases, classify the data involved, define approval criteria, assign owners, and build a prioritized action plan. The immediate output should be practical: an initial inventory, a draft acceptable-use position, high-risk use cases that need action, and a clear route for evaluating new tools.
Computerbilities helps small and midsize organizations connect everyday IT management, cybersecurity, cloud applications, and business planning. Schedule an AI governance workshop to map where AI is already in use, reduce AI data leakage risk, and create guardrails that support productive, accountable adoption. Computerbilities serves businesses in Raleigh, Cary, Durham, the NC Triangle, and New York City.
Frequently Asked Questions
What is shadow AI
Shadow AI is the use of AI tools or AI-enabled features for business work without the organization’s approval, management, or visibility. It can include public chatbots, meeting assistants, coding tools, browser extensions, embedded software features, and agents connected to company systems.
How can generative AI leak company data
Data can leak through prompts, file uploads, retained chat history, broad integrations, insecure outputs, shared links, model or application misconfiguration, and automated actions. The exact risk depends on the service, account type, settings, contract, connected systems, and information used.
Should employees be banned from using public AI tools
A business may prohibit public tools for certain data or tasks, but a blanket ban is difficult to enforce and can push use into personal accounts. A stronger program combines approved options, clear data rules, training, technical controls, monitoring, and a fast process for reviewing legitimate requests.
What information should never be pasted into an unapproved AI tool
Employees should not enter credentials, security keys, regulated personal information, customer records, confidential contracts, source code, incident details, legal advice, unreleased financial information, or trade secrets into an unapproved service. The organization’s data classification and AI use policy should provide more specific rules.
What is the first step in reducing shadow AI risk
Start with discovery. Build an inventory of tools, embedded AI features, users, use cases, data, and integrations. Then prioritize the combinations with sensitive data, broad permissions, external publication, automated actions, or important decisions. The inventory gives policy and control work a factual starting point.
Who should own AI governance
Executive leadership should assign accountable ownership, but AI governance usually requires several functions. IT and security manage technology and access; privacy and legal interpret obligations; business owners define the purpose and acceptable outcomes; procurement manages vendor terms; and employees follow the approved process. A managed or co-managed IT partner can help a smaller organization coordinate the technology inventory, access controls, vendor review, training, and monitoring that support those responsibilities.